EditionsAustralia EditionIndia EditionSingapore EditionUnited KingdomUnited States doFir.push(function(){if(getCookie('nwsubl')){jQuery(".login-btn .sign-up2").hide();jQuery(".login-btn .myaccount").show()};jQuery(".login-btn .myaccount").on('click',function(e){e.preventDefault();jQuery(".login-btn ul").toggle()});jQuery(document).ready(function(){jQuery(".myaccount").add(".m-manage").each(function(){jQuery(this).attr('href','https://myaccount.ibtimes.co.uk/manage')})})}) googletag.cmd.push(function () { if(dfpSlots.slotobjs["top"]){ ibt_log("ADS GPT register ad slot top", Date.now()-timerStart); googletag.display("dfp-ad-top"); } });if(/top\|[0-1]\|1/.test(dfpSlots.pginfo[ibtmedia_device])) document.getElementById("ad-top-wrapper").className+=" block-sticky" CYBERSECURITY dfpSlots.vplayer=(['ibtuk','ibtus'].indexOf(site_id)>-1)?'primis player':'NoVideo';if(site_id=='ibtuk'&&oa.geo.country!='IL'&&ibtmedia_device=='mobile')dfpSlots.vplayer='NoVideo';if(/adtest=primis/.test(location.href))dfpSlots.vplayer='primis player';else if(/adtest=native/.test(location.href))dfpSlots.vplayer='ibt player';if(dfpSlots.vplayer=='primis player'){if(site_id=='ibtus'){dfpSlots.primis='117767'}else dfpSlots.primis='117814';dfpSlots.primisVideo=function(){if(dfpSlots.primisVideoLoaded)return;dfpSlots.primisVideoLoaded=1;if(adBlock=='Y')return;var d=document,gi='getElementById',s=d.createElement('script');s.type='text/javascript';s.src='https://live.primis.tech/live/liveView.php?s='+dfpSlots.primis+'&cbuster='+Date.now();if(window.ibt_avf){ibt_avf.appendChild(s);d.body.classList.add('video-primis')}else d[gi]('tvplayer').appendChild(s)}} if(dfpSlots.vplayer=='NoVideo'&&document.getElementById('ibt-mobile-avf'))document.getElementById('ibt-mobile-avf').remove();oa.pageinfo.VideoABTest=dfpSlots.vplayer;var ibt_avf=(brW
The exposed records reportedly include names, email addresses, phone numbers, home addresses and order details, with the Trump Organization's own chief information officer among those listed.
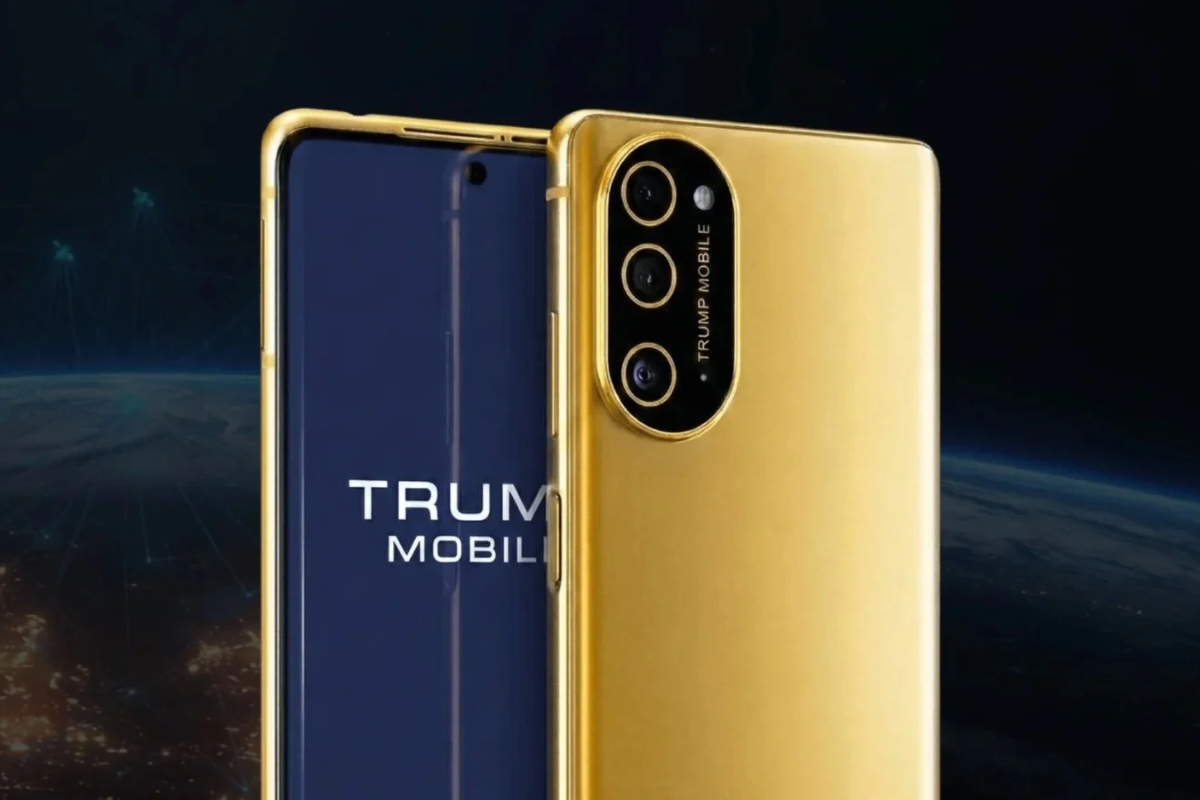
To recall, this is not the first security scare for the politically branded MVNO. In May 2026, two YouTubers flagged an exploitable flaw on TrumpMobile.com that could have leaked similar customer information, though the company said at the time it found no evidence its systems were compromised.
According to Straight Arrow News, which first reported the incident, a representative for BYOD told the outlet the group gained access after infecting an employee at Florida-based Liberty Mobile with malware. Liberty Mobile is known to power Trump Mobile, which is owned by T1 Mobile and uses branding licensed from the Trump Organization.
The attackers claimed they installed a Remote Access Trojan on the target's device, then pivoted to exposed Trump Mobile subdomains to exfiltrate customer data.
This article was aggregated automatically by CyberWire Daily's newsfeed engine. Original reporting: www.ibtimes.co.uk.